What is CGNAT and why your IP might be shared
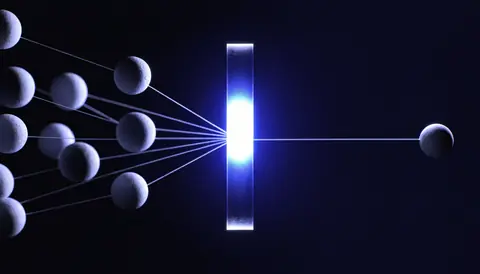
Carrier-grade NAT, or CGNAT, is a way for an internet provider to put many customers behind a single public IP address. If you are on it, the address that websites see is not yours alone. It is shared with other households or phones on the same provider.
For browsing, streaming, and video calls, you will not notice. It becomes a problem when something outside needs to start a connection to you: hosting a game, reaching a home camera, or running a server. This guide explains why providers use it, how to check whether you are behind it, and what your options are.
Why providers use it
There are not enough IPv4 addresses to give every customer one. IPv4 has room for about 4.3 billion addresses, the central pool of unassigned blocks is used up, and buying more on the open market is expensive.
Home routers already solved a version of this problem. With ordinary NAT, every device in your home shares the one public address your router holds. See public vs private IP addresses for how that works.
CGNAT applies the same trick one level higher. Instead of giving your router a public address, the provider gives it an address from a reserved range and runs a large NAT gateway in its own network. That gateway holds the public addresses and shares each one between many customers.
The gateway tells customers apart the same way your home router tells devices apart: by port number. Each customer’s outgoing connections are given a slice of the ports on the shared address.
It is also called large-scale NAT, or NAT444 when describing the full path: private address in the home, shared address at the provider, public address on the internet.
The address range to look for
A dedicated block is set aside for the link between your router and the provider’s gateway:
100.64.0.0/10That covers 100.64.0.0 through 100.127.255.255. It is defined in RFC 6598 as shared address space. It behaves like a private range but is kept separate from the home ranges so that it cannot clash with whatever your own router uses inside.
Enter the block in the Subnet Calculator to see its exact boundaries.
How to tell if you are behind CGNAT
You need two addresses to compare.
- Find your public address. Turn off any VPN, then open the WebIPTool home page and note the IPv4 address.
- Find your router’s internet-side address. Sign in to your router and look for a page called Internet, WAN, or Status. Our guide to finding your router’s IP address explains how to get to the settings page.
- Compare them.
| What you see on the router’s WAN page | What it means |
|---|---|
| The same address as the home page | You have your own public address. No CGNAT. |
An address from 100.64.0.0 to 100.127.255.255 |
CGNAT, using the standard shared range. |
An address starting with 10., or in 172.16. to 172.31. |
CGNAT using a private range, or a provider gateway or second router in front of yours. Check that box’s WAN address too. |
An address starting with 192.168. |
Usually a second router or the provider’s modem in front of yours, not CGNAT. Check that box’s WAN address too. |
| Any other address that differs from the home page | Some form of NAT upstream. Ask your provider. |
On mobile data you can assume CGNAT. Nearly all mobile networks use it for IPv4.
What works normally
Anything where your device starts the conversation works as usual:
- Web browsing, email, and streaming
- Video calls and messaging
- Online gaming as a player, in most cases
- Outgoing VPN connections
These services are built with NAT in mind, since home routers have used it for decades.
What CGNAT gets in the way of
Port forwarding. You can add a forwarding rule in your own router, but incoming connections stop at the provider’s gateway and never reach it. This is the main practical limitation.
Hosting from home. Game servers, web servers, self-hosted services, and remote access to cameras or a home lab all rely on outside connections reaching you.
Peer-to-peer connections. Some games and apps connect players directly to each other. Behind two layers of NAT that is harder, and consoles may report a “strict” or “type 3” NAT. Matchmaking can be slower and voice chat less reliable.
Reputation of the shared address. If another customer on your address sends spam or abusive traffic, sites may respond with extra CAPTCHAs or temporary blocks for everyone behind it.
Allow-lists. If a service only accepts connections from an address you registered, a shared address that also changes will not work well.
Location accuracy. The public address belongs to the gateway, which may be in another city. Location lookups point there. More on this in what your IP address reveals.
What you can do about it
Ask for a public address
Some providers will move you off CGNAT on request, either for free or as a paid add-on, often described as a static IP or a public IP option. Business plans often include one. This is the cleanest fix if it is available.
Use IPv6
CGNAT only affects IPv4. If your provider offers IPv6, your devices get public IPv6 addresses with no sharing involved, and incoming connections are possible once you open the one port you need, for the one device that needs it, in your router’s firewall. Leave the rest of the IPv6 firewall on.
The catch is that whoever is connecting to you also needs IPv6. That is increasingly common but not universal. The home page shows whether your connection has IPv6. For background, see IPv4 vs IPv6.
Use a relay or tunnel
If you cannot receive incoming connections, you can make an outgoing one to a server that can, and have it pass traffic back to you. There are several forms of this:
- A tunnelling service that gives you a public address or hostname and relays connections to your device.
- A mesh VPN that connects your own devices to each other wherever they are.
- A VPN service that includes port forwarding.
- A small rented server with a public address, used as your own relay.
All of them work because CGNAT does not interfere with connections you start from inside.
Change how the service is hosted
Sometimes the practical answer is to host the service somewhere else, on a rented server or a hosted platform, and connect to it from home like any other site.
Is CGNAT a privacy benefit?
A little, as a side effect. Outsiders see an address shared by many people, so it says less about you individually.
It is not anonymity. Providers that run CGNAT keep records that map each connection back to a customer, typically by logging the address and port range in use at a given time. The operational requirements for these gateways, including logging, are described in RFC 6888.
Key points
- CGNAT shares one public IPv4 address between many customers, because IPv4 addresses are scarce.
- If your router’s WAN address differs from the address websites see, with any VPN off, something upstream is doing NAT. A WAN address in
100.64.0.0/10confirms CGNAT. - Outgoing connections work normally. Incoming connections, port forwarding, and home hosting do not.
- The fixes are a public address from your provider, IPv6, or a relay that you connect out to.